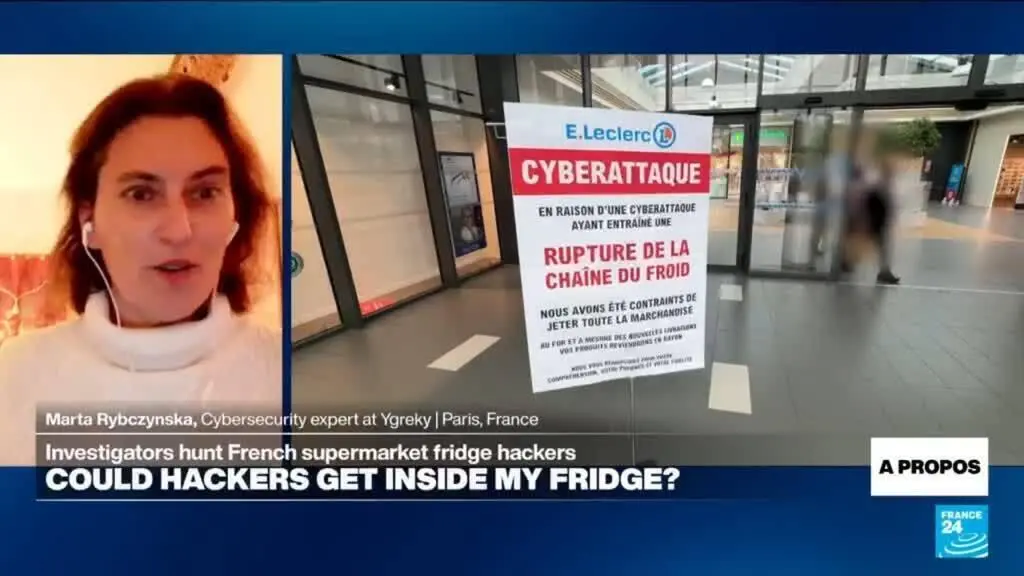
How Hackers Gained Access to Cooling Systems
French investigators revealed on Tuesday that cybercriminals successfully took control of refrigeration units in multiple supermarkets due to fundamental security oversights. The attacks, which occurred across several retail chains, allowed hackers to manipulate temperature settings and potentially compromise food safety. Security experts warn that outdated systems and missing basic protections left these critical infrastructures vulnerable to intrusion.
The breach highlighted how attackers exploited weak default passwords and unpatched software in supermarket cooling systems. Investigators noted that many units remained connected to internal networks without proper segmentation or firewall protections. Cybersecurity officials emphasized that these systems often run on legacy operating systems with known vulnerabilities that were never updated. The incident prompted immediate audits of similar equipment nationwide to identify other at-risk installations.
What Steps Are Being Taken to Prevent Future Incidents
Investigators explained that hackers used brute-force techniques to guess simple passwords on administrative interfaces exposed to the internet. Once inside, they deployed malware that gave them remote control over temperature regulators. Some attackers reportedly adjusted settings to cause gradual warming, risking spoilage of perishable goods while avoiding immediate detection. The method demonstrated how seemingly minor oversights could lead to significant operational disruptions.
Authorities have mandated that all supermarket chains implement multi-factor authentication and network isolation for industrial control systems within 30 days. Retailers are now required to conduct quarterly penetration tests on connected equipment and maintain detailed logs of all access attempts. Cybersecurity agencies are also developing standardized security templates specifically for refrigeration units to ensure consistent protection across the sector.
How did hackers initially access the supermarket fridges? They exploited weak or default passwords on remotely accessible administrative panels, using automated tools to guess credentials and gain entry to the control systems.
Frequently Asked Questions
What was the main goal of these cyberattacks? While investigators believe the primary aim was to demonstrate system vulnerabilities, the manipulation of temperatures posed a real risk to food safety and could have led to financial losses through spoiled inventory.
Are consumers at risk from these incidents? Direct health risks are considered low as attacks were detected quickly, but the incidents underscore the importance of securing critical infrastructure to prevent potential future threats to food supply chains.